The Six-Week Fix That Took 30 Minutes
AI is compressing the time between finding a software vulnerability and repairing it.
Chris MachutRead the article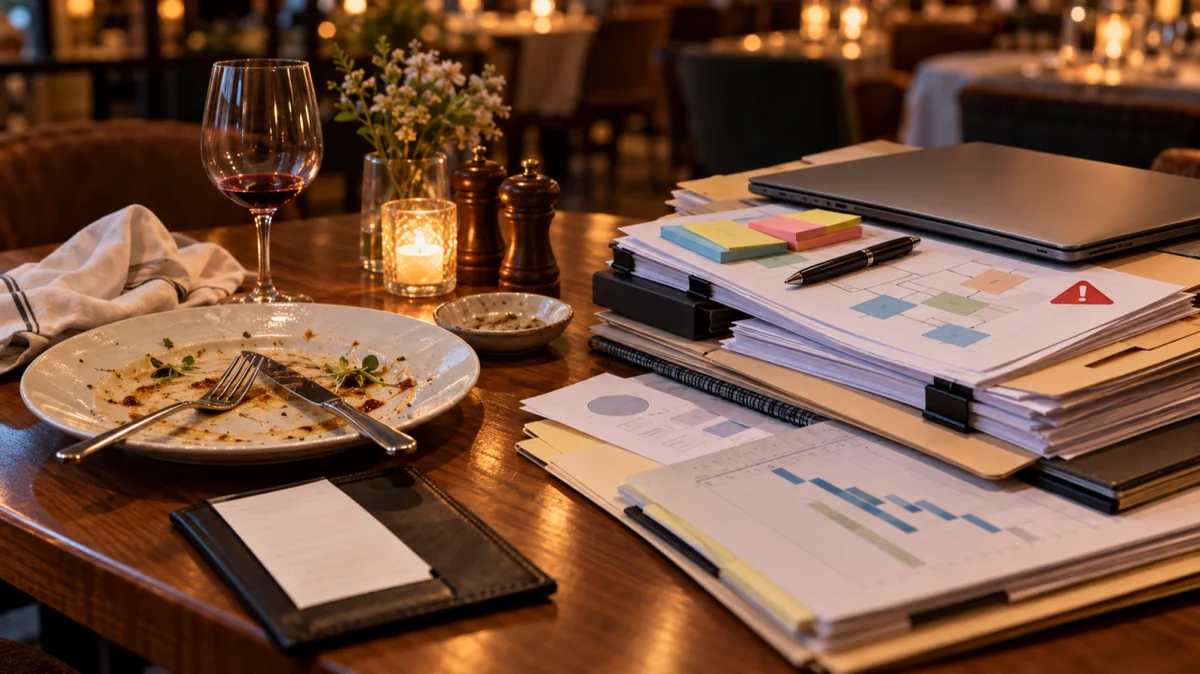
AI is compressing the time between finding a software vulnerability and repairing it. The harder question is whether the way companies manage risk can move just as quickly without giving up sound judgment.
Thirty Minutes Over Dinner
Over dinner recently, a friend who has spent about 25 years in enterprise technology told me about a legacy system that had suddenly become a very current problem. It was running on PHP infrastructure deployed roughly 15 years ago, and a vulnerability had left the team facing the kind of decision that makes old software expensive long after anyone remembers why it was built that way.
The traditional response would have been familiar. Turn off the system, scope the work, build a sprint plan, update the code, test it and work through deployment. He estimated that the application could have been offline for six weeks while all of that happened. In a large organization, six weeks might not even sound unreasonable. It might sound responsible.
This time, he asked AI to upgrade the application to the latest version of PHP 8, recode what needed to change and preserve the existing functionality. About 30 minutes later, the work was complete enough to send to the customer. The customer asked the question customers usually ask when the technical explanation is longer than their patience: “Does it work?” My friend said yes. The customer told him to deploy it.
I kept coming back to the distance between those two numbers: six weeks and 30 minutes. This was not proof that every legacy application can be rebuilt before the dinner check arrives, and it did not mean testing or human review had become optional. It was a sign that the time required to produce a viable remediation could collapse, even while the process surrounding that work remained built for a slower era.
That matters because the software industry has grown comfortable with long exposure windows. We open a ticket, estimate the work, find room in a sprint and move the change through testing and approval. Each step may be sensible on its own, but the vulnerability does not pause while the organization gets organized. The old process can be careful and still be too slow.
A Well-Timed Interruption
A few days later, I was on a call with some some members on our team. We began with the ordinary mechanics of collaborative work: locating documents, sorting out access and determining which draft belonged to whom. AI may be able to rewrite a legacy application in half an hour, but it has apparently not yet rescued us from version control by filename.
One of our leads joined late and apologized. “Ironically, a security incident,” she said. Her security tools had flagged zero-day issues, including some that showed signs of exploitation. What was supposed to be a planning conversation had been interrupted by the exact problem we were there to discuss.
She described a steep rise in the number of security findings his team was seeing. They were managing to keep the open backlog relatively flat, but only through substantial investment and AI-driven agents that helped them address issues at scale. We called it whack-a-mole, although the arcade version now seems almost relaxing - at least the moles waited their turn.
The more important point was not the number of alerts. It was that discovery and remediation were both accelerating. AI could surface weaknesses that might once have remained buried in old code, but finding more problems faster only helped if an organization could also evaluate and repair them faster.
The conversation also offered an important warning about that speed. She had used AI to help draft a security planning document for the group, while our other teammates had developed their own version and gathered material that she thought could strengthen it. She was uneasy with how confidently the AI-generated draft presented conclusions that neither of them had fully examined or agreed to. The draft was useful because it gave the group something concrete to challenge, combine and improve. It was not useful because a machine had supposedly settled the issue.
That is the tension companies now have to manage. AI can help inspect unfamiliar code, identify a weak point, propose a repair, rewrite a component and generate tests far faster than the traditional cycle allowed. It can also produce an answer that sounds complete before the people responsible for the outcome have decided whether it is correct. Speed changes the work, but it does not transfer accountability.
The Hall Pass
For years, the industry operated with what I described on the call as a hall pass. Vulnerabilities could be discovered, disclosed and addressed through processes that often gave defenders at least some breathing room. The work was rarely comfortable, but the clock was usually measured in days, weeks or sprint cycles.
That "hall pass" is gone.
AI can be used to search for weaknesses, study unfamiliar systems and adapt attack methods across more targets. Defenders can use the same class of technology to find vulnerable code, propose fixes and test repairs. The question is not whether both sides will use it. The question is how quickly individual organizations can respond without creating a second problem in their rush to solve the first.
This does not mean a company should hand production access to an AI agent and hope for the best. Legacy systems contain hidden dependencies, undocumented integrations and business rules that may live mostly in the memory of one employee who was hoping to take Friday off. A fast PHP upgrade can still break authentication, reporting, data handling or a customer workflow.
The lesson from the dinner conversation was not that judgment no longer matters. It was that judgment cannot become an excuse for avoidable waiting.
The business stakes are straightforward. A vulnerable system can interrupt operations, expose customer data, increase recovery costs and damage trust. A rushed fix can do many of the same things. The advantage will not belong to the company that moves fastest at any cost. It will belong to the company that learns how to shorten the exposure window while keeping the controls that actually protect the business.
One System, One Clock
A practical first move is to choose one aging or exposed application and run a controlled AI-assisted remediation exercise. Put a copy in an isolated environment, map the dependencies, let AI propose an upgrade or patch, and require automated testing and qualified human review before anything reaches production. Make sure the team has a rollback plan, because confidence is not the same thing as proof, whether it comes from a person or a model.
Then measure the part that matters: the time from discovering the vulnerability to producing a tested remediation candidate. That number will reveal where the real delay lives. It may be in the code, but it may also be in ownership, access, testing, approvals or the simple fact that nobody decided in advance who was allowed to act.
Thirty minutes is not a universal benchmark, and one dinner story does not settle how every company should use AI in security. But it does reset the question. If work that once required a six-week sprint can sometimes be reduced to the length of a meal, leaders should know which parts of their remediation cycle are protecting the business and which parts are simply keeping the table occupied.
Related work
Find this in the history
Before an AI Agent Acts in the Yard
Before an AI agent answers a pickup inquiry or acts in a yard, verify the asset, the freshness and source of the evidence, and who has authority to act.
When Intelligence Becomes a Commodity, Reality Becomes the Moat
The better AI gets, the less simply having AI will matter. That sounds contradictory, but I think it is where the market is heading.
Spire: The Five Keys To Business Bliss
In this podcast and article on ThoughtLeadership.biz, Mr. Machut talks about nurturing our creative energies and engaging in meaningful learning activities to increase wellbeing.